Xander Franke · 11 September 2026
Navigating Data Privacy Challenges During Platform Integrations for Performance Tracking
Platform integrations for performance tracking connect analytics tools, customer relationship management systems, and reporting dashboards so organizations can measure campaign results and user engagement across channels, yet these connections often move large volumes of personal data that must comply with multiple privacy frameworks at once.
Regulatory Landscape for Data Transfers
Organizations face overlapping requirements from the European Union's General Data Protection Regulation, the California Consumer Privacy Act, and Canada's Personal Information Protection and Electronic Documents Act, each of which sets rules for consent, data minimization, and cross-border transfers that become more complex when platforms share data in real time. Research from the Federal Trade Commission shows that enforcement actions have increased when companies fail to maintain clear records of data flows during such integrations, and similar patterns appear in reports issued by the Office of the Privacy Commissioner of Canada.
Performance tracking platforms typically exchange identifiers such as device IDs, IP addresses, and behavioral signals, which means integration teams must map every data element to its legal basis for processing before any connection goes live.
Technical and Operational Hurdles
Legacy systems often store data in formats that do not support granular consent flags, so engineers must rebuild data pipelines to tag each record with purpose limitations and retention schedules. When two platforms merge their datasets, duplicate entries can appear that complicate deletion requests under laws that grant individuals the right to be forgotten, and auditors have documented cases where mismatched schemas led to incomplete responses to access requests.
Encryption standards also vary between vendors, which creates gaps during transmission unless teams enforce uniform protocols such as TLS 1.3 across every endpoint. Observers note that September 2026 marks the expected rollout of updated technical standards from several international standards bodies, requiring organizations to audit their encryption configurations well in advance to avoid service disruptions.
Consent Management Across Connected Systems
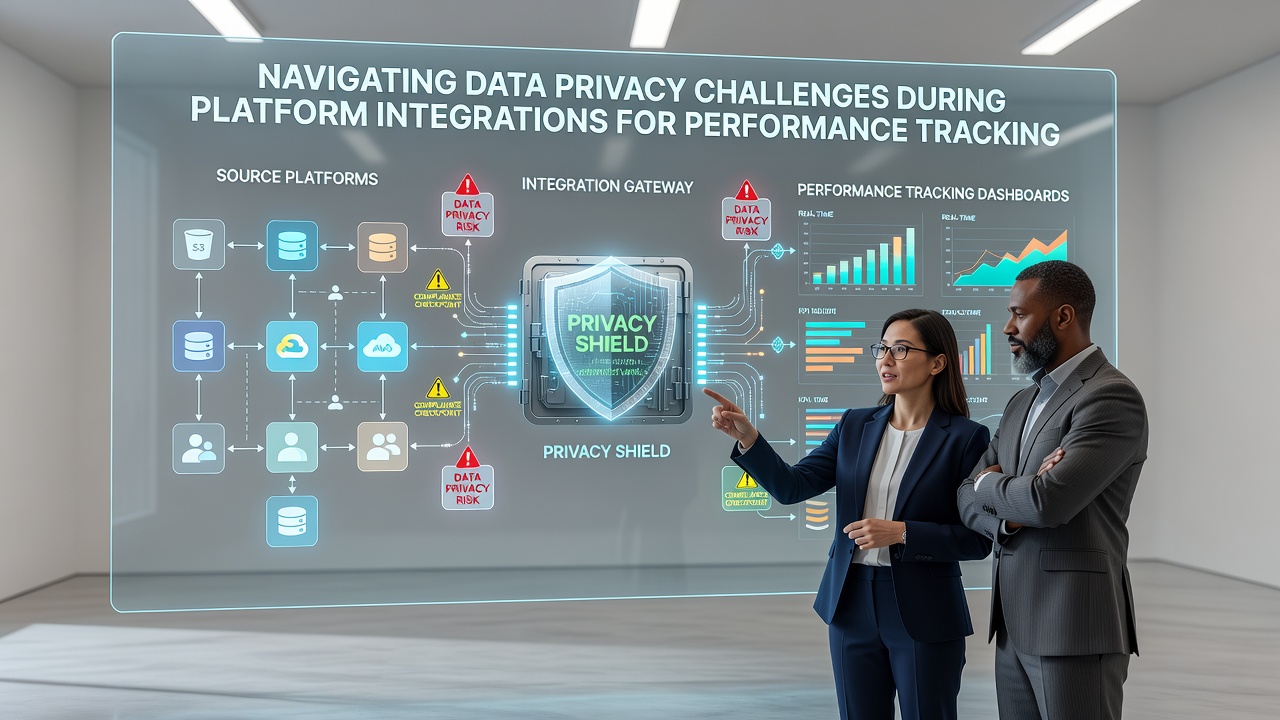
Consent collection becomes fragmented when users interact with multiple touchpoints that feed into a single performance dashboard, so companies deploy centralized consent management platforms that push updated preferences to every connected system through APIs. Data indicates that organizations using these platforms reduce the time needed to honor opt-out requests from days to minutes, yet they must still verify that downstream vendors honor those signals without delay.
Third-party pixels and tracking scripts embedded during integration can collect data outside the primary consent framework, which prompts compliance teams to maintain inventories of every script and to test whether each one respects user choices. Studies from academic research groups have found that unvetted scripts account for a significant share of privacy complaints filed after platform mergers.
Practical Steps Taken by Compliance Teams
Teams begin with data mapping exercises that list every field transferred between platforms and assign a lawful basis such as contract necessity or legitimate interest, then they configure access controls so only authorized personnel can view or export those fields. Regular penetration tests and privacy impact assessments uncover vulnerabilities before they affect live data, while automated monitoring tools flag unusual transfer volumes that might signal a breach.
Vendor contracts now routinely include data processing addenda that specify audit rights and breach notification timelines, and procurement departments review these clauses before approving new integrations. Figures from industry reports reveal that companies completing such reviews before launch experience fewer post-integration compliance issues than those that treat contracts as an afterthought.
Outlook Through 2026 and Beyond
Regulators in multiple jurisdictions continue to issue guidance on automated decision-making and profiling that directly affects performance tracking dashboards, which means integration roadmaps must include checkpoints for emerging rules. Organizations that maintain living documentation of data flows and conduct quarterly reviews stay ahead of these changes, whereas those relying on static policies encounter repeated remediation cycles.
Conclusion
Platform integrations for performance tracking deliver measurable efficiency gains when privacy controls are built into the connection process from the start, and evidence from regulatory filings shows that proactive mapping, consent synchronization, and vendor oversight reduce both enforcement risk and operational friction. As standards evolve through September 2026 and afterward, teams that treat data privacy as a core engineering requirement rather than a separate compliance task maintain smoother data pipelines and stronger user trust across connected systems.