Vera Frank · 23 October 2026
Exploring Encryption Standards for Cross-Platform Data Transfers in Business Intelligence Tools
Business intelligence tools handle large volumes of sensitive information that moves between different systems and vendors on a regular basis, and encryption standards play a central role in protecting that movement. Organizations rely on established protocols to safeguard data during transfers, while maintaining compatibility across platforms that run on varied operating systems and cloud environments.
Core Encryption Protocols in Use Today
Advanced Encryption Standard with 256-bit keys remains a foundational choice for securing data at rest and in transit within BI ecosystems, according to specifications from the National Institute of Standards and Technology. Transport Layer Security version 1.3 provides the primary mechanism for protecting data streams between servers and client applications, reducing vulnerabilities that earlier versions exposed during handshake processes. Researchers at institutions such as the University of Waterloo have documented how these combined approaches limit exposure windows when datasets cross organizational boundaries.
Many platforms integrate additional layers such as AES-GCM for authenticated encryption, which simultaneously verifies integrity and confidentiality. This matters because BI environments often pull from multiple sources simultaneously, creating numerous points where interception could occur without proper safeguards.
Cross-Platform Compatibility Challenges
Data transfers between BI tools hosted on different infrastructures introduce friction points around key management and algorithm support. One platform might default to certain cipher suites while another enforces stricter policies, leading teams to negotiate common standards that satisfy both sides. Studies from the European Union Agency for Cybersecurity indicate that mismatches in protocol versions account for a measurable portion of transfer failures in multi-vendor setups.
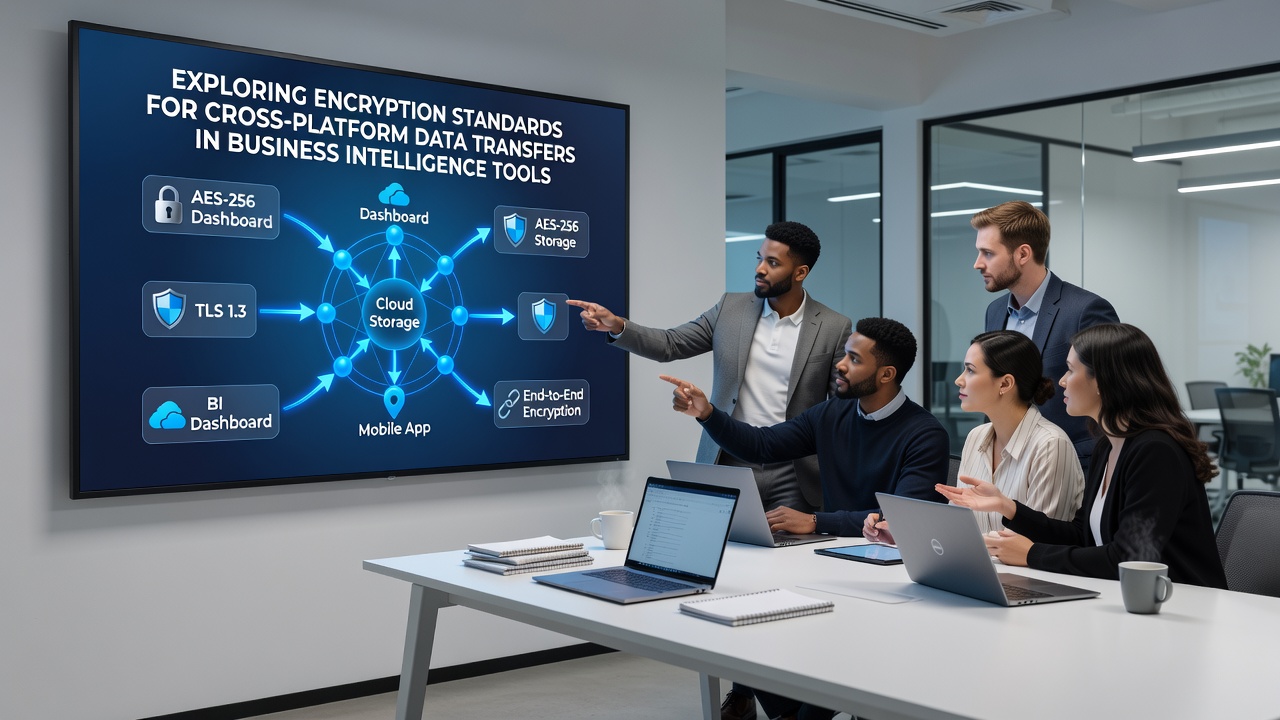
Key exchange mechanisms like Diffie-Hellman and elliptic curve variants help establish shared secrets without transmitting them directly, yet implementation differences across operating systems can still create gaps. Observers note that organizations frequently standardize on TLS 1.3 with specific cipher preferences to minimize these issues, though legacy systems sometimes require fallback options that weaken overall protection.
Regulatory Influences adn Implementation Patterns
Government frameworks shape how companies apply encryption during transfers. Canadian authorities have issued guidance that aligns closely with international standards while adding requirements for logging and audit trails. In October 2026 several BI vendors released updates that incorporated these regional expectations alongside core protocol improvements, allowing smoother compliance across North American and European deployments.
Industry reports show that organizations using centralized key management services experience fewer disruptions when moving data between tools. These services handle rotation schedules and access controls, reducing the chance that expired keys interrupt scheduled transfers or ad-hoc queries that span platforms.
Emerging Approaches and Ongoing Adjustments
Post-quantum cryptography preparations have begun appearing in some BI vendor roadmaps, though widespread adoption remains limited as of late 2026. Hybrid schemes that combine classical algorithms with newer lattice-based methods allow gradual transitions without breaking existing cross-platform workflows. Data from academic trials suggests these hybrids maintain performance levels close to current standards while adding resistance against future quantum threats.
Teams that document their encryption configurations across every connected system find it easier to audit transfers and respond when standards evolve. Automated scanning tools now detect cipher deprecations and flag them before they affect production data movement.
Conclusion
Encryption standards continue to evolve alongside the platforms that depend on them, with cross-platform data transfers in business intelligence environments requiring careful alignment of protocols, key practices, and regulatory expectations. NIST guidelines and ENISA recommendations provide reference points that many organizations consult when updating their configurations, while October 2026 updates from vendors demonstrated ongoing refinement in this area. Consistent application of these measures supports secure movement of information without creating unnecessary barriers between systems.